
End-to-end TLS 1.3
Every endpoint is encrypted with TLS 1.3 + HSTS + cert pinning — no MITM possible. Cloudflare WAF guards against DDoS.
A+
SSL Labs Rating
PDPA-first design · every endpoint encrypted · slip images deleted within 60 seconds · audit log for every event
Every endpoint is encrypted with TLS 1.3 + HSTS + cert pinning — no MITM possible. Cloudflare WAF guards against DDoS.
Customer slip images are deleted within 60 seconds after verification — only the required text data is retained.
Tokens live in httpOnly cookies, not localStorage — far better XSS protection, with refresh rotation every 7 days.
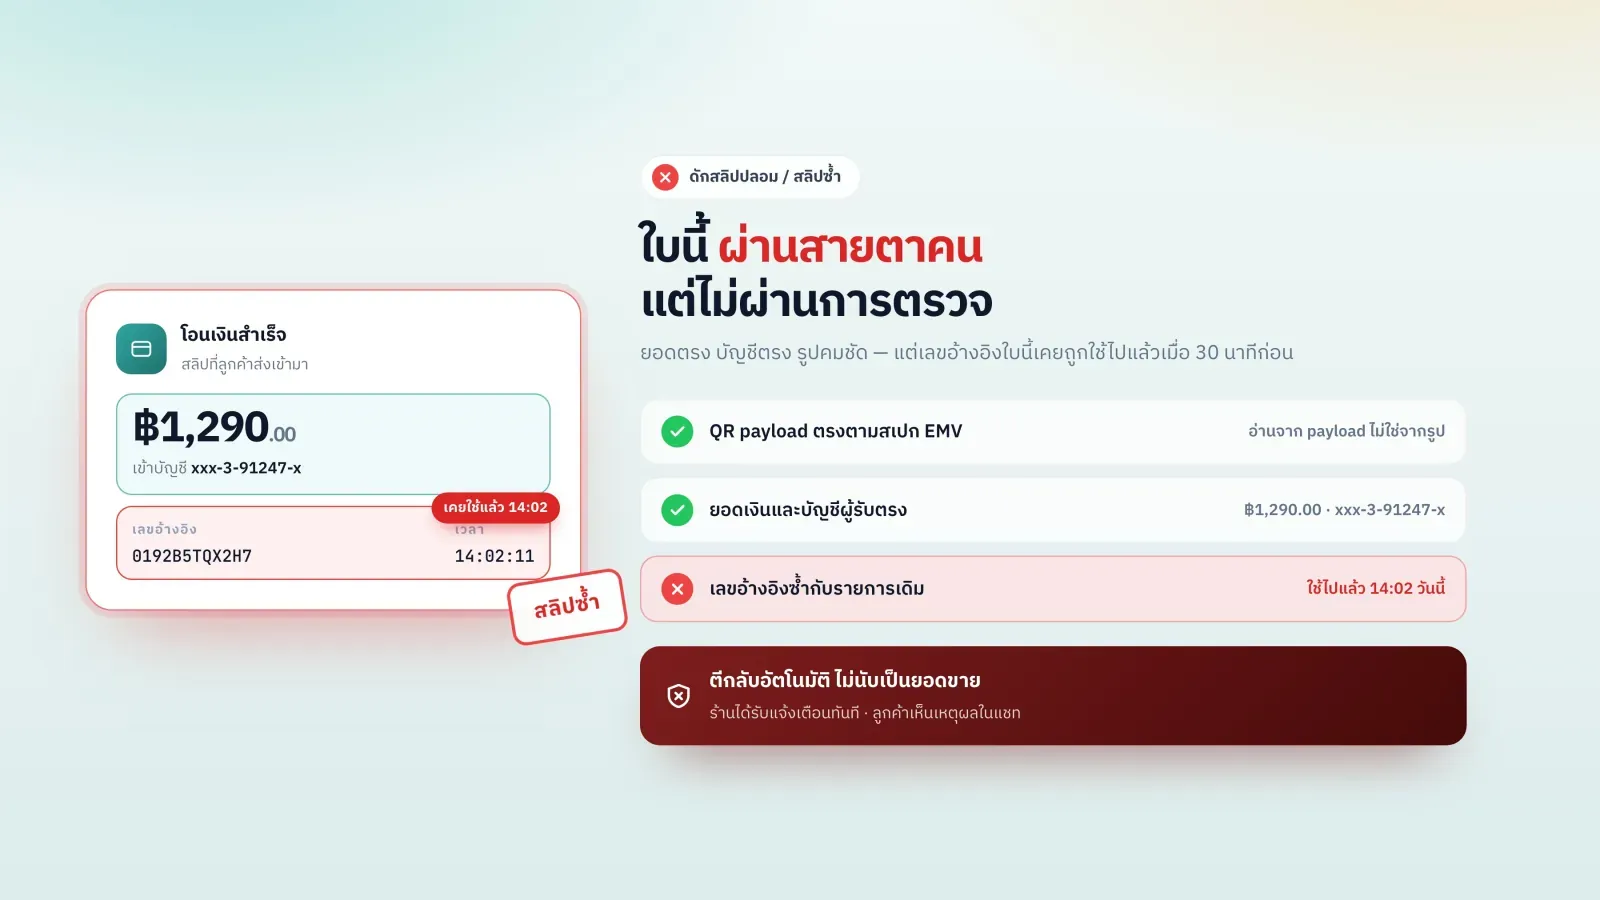
Every slip is protected by a unique constraint in MariaDB + Redis cache — recycled or duplicate slips are caught in a split second.
Per-shop rate limits prevent abuse and brute force via Redis-backed @nestjs/throttler.
Every action in the Dashboard and API is recorded with actor / IP / timestamp — downloadable as CSV.
There is more in a slip than the eye reads. These are the four things SlipBolt checks every time — pick one to see where it lives.
See exactly where your customers' data travels — and where it gets deleted.
Thailand's Personal Data Protection Act B.E. 2562
EU General Data Protection Regulation
Information Security Management — Q2 2026
via Stripe payment processor
Under Thailand's Personal Data Protection Act (PDPA) you always have rights over your data — SlipBolt is designed so you can exercise them directly from the Dashboard in a few clicks.
